Pwn2Own: Samsung Galaxy S26 Hacked via a Single Email
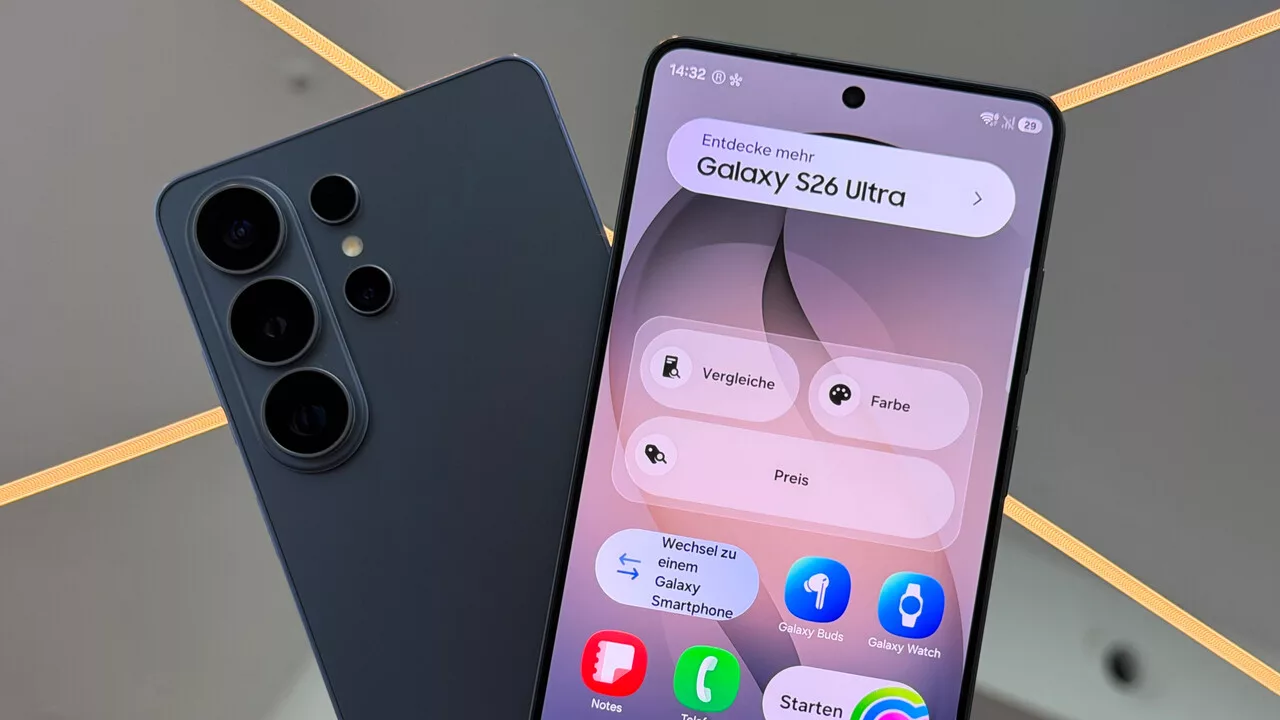
During the Pwn2Own hacking competition in Ireland, security researchers demonstrated remote code execution on a Samsung Galaxy S26 smartphone. The team from the Japanese firm Ikotas Labs utilized four zero-day vulnerabilities to achieve the exploit, proving that a single malicious email could be enough to compromise the device.
Attack Vector and Vulnerabilities
As reported by SammyGuru citing the Zero Day Initiative (ZDI), one of the four vulnerabilities used was already known but had not yet been patched by Samsung. Following the successful demonstration, Ikotas Labs was awarded a $11,000 prize.
Ikotas Labs CEO Stoki Tsuji explained that the attack combined the delivery of an infected email with a separate method for local privilege escalation. This combination allowed for remote code execution on the Galaxy S26. However, it remains unclear whether the user needed to actively open the email or interact with its content to trigger the exploit.
Other Targets and Patching
The Samsung Galaxy S26 was not the only device compromised at the event. Ikotas Labs also successfully attacked a Google Pixel 10. While the specific details of the exploit for the Pixel are not available, the team earned a much larger prize of $300,000 for this feat. Technical details regarding the exploits are being withheld until Samsung and Google release security updates to fix the identified vulnerabilities.
Гика